
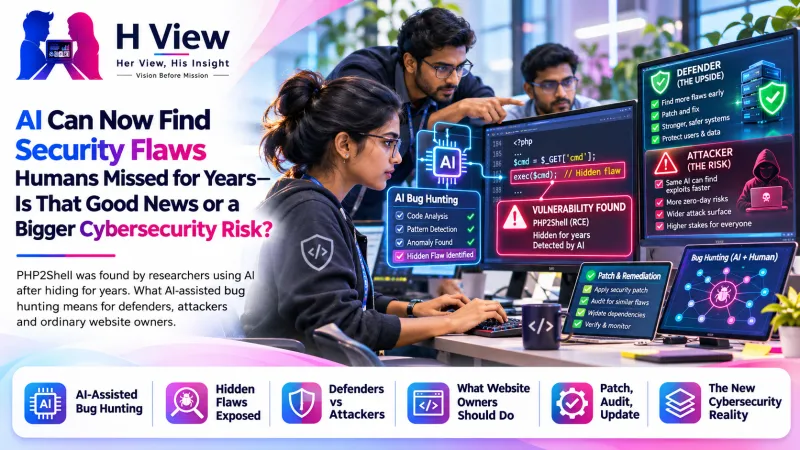
AI Can Now Find Security Flaws Humans Missed for Years—Is That Good News or a Bigger Cybersecurity Risk?
The flaw that knocked government websites offline was found with AI help. Does that make the internet safer, or give attackers a faster weapon? Honestly, both.
Short answer: It is both. AI can help researchers find security flaws that hid for years, as the PHP2Shell flaws showed in October 2026. But the same tools help attackers turn a published fix into a working attack faster. The net result depends on who patches faster: defenders or attackers.
Last reviewed: 4 November 2026.
For decades, finding a serious bug inside a programming language used by millions of websites took rare human expertise, patience and a fair bit of luck. In October 2026, that changed in a very public way. The PHP2Shell flaws, which led governments, banks and hospitals around the world to take systems offline for emergency patching, were found by security researchers working with AI tools. That raises a question worth sitting with: is this the start of a safer internet, or a more dangerous one?
How AI helped find PHP2Shell
Two separate teams arrived at the problem. Security firm Calif found the flaws as part of an OpenAI programme that gives researchers advanced AI models for finding vulnerabilities, and Calif credited an independent researcher with first discovering the issue and building a working exploit. Cybersecurity firm Wiz independently found and reported the same flaws starting on 19 August, using tools including Wiz Atlas, Google's Gemini and OpenAI's models.
What makes the story striking is how long the weakness had been sitting there. E-commerce security firm Sansec reported that the vulnerable code dates back to PHP 5.4, released in 2012. Calif even said it had not expected to find critical issues, because many people had already run AI-assisted audits of PHP. Wiz's co-founder Ami Luttwak described it as the most severe vulnerability ever found with AI assistance, and suggested it was likely too complex to have been found without it.
Why this is genuinely good news
Old, hidden bugs get found and fixed
Software that runs the internet is enormous, and much of it is maintained by small volunteer teams. AI can read and reason about huge codebases far faster than any person, flagging the odd crash or strange memory behaviour that might hide a serious flaw. Every bug found by a researcher is one less bug waiting for a criminal.
Defenders get a force multiplier
Most organisations cannot afford a team of elite security researchers. AI-assisted tools can bring some of that capability within reach of smaller companies and open-source projects, helping them review code, triage reports and test fixes.
Humans stay in the loop
Researchers describe PHP2Shell as found by people using AI, not by AI alone. Every result was checked by hand. That is the healthiest model: AI widens the search, experts decide what is real.
 Also readAI Agents vs Chatbots: What Is the Difference for Everyday Users?→
Why it is also a bigger risk
Attackers move faster too
Tenable said exploitation attempts were seen within hours of the PHP2Shell disclosure. Calif's chief executive Thai Duong warned that anyone could take the published patches, point AI at them and work out an attack. OpenAI itself said the same capabilities that help defenders can help attackers build exploits quickly.
Maintainers are being flooded
As AI makes bug hunting cheaper, projects like PHP are receiving a growing stream of reports. Not every report is serious, and sorting the urgent from the trivial takes scarce human time.
The patching gap matters more than ever
Hundreds of thousands of servers still run PHP versions that get no official fix. When discovery speeds up but patching doesn't, the window of exposure becomes the real danger.
Good news or risk? A side-by-side view
| Area | How AI helps defenders | How AI helps attackers |
|---|---|---|
| Finding bugs | Surfaces flaws hidden for years | Could find unknown flaws to keep secret |
| After a patch | Speeds up testing of fixes | Speeds up reverse-engineering patches into exploits |
| Scale | Small teams can audit more code | Small groups can attack more targets |
| Bottleneck | Human review and patch rollout | Finding unpatched systems, which is easy |
What this means for ordinary website owners
You don't need to understand memory-safety bugs to protect yourself. You need to shorten the time between a fix being released and your site using it:
- Use a hosting provider that applies security updates quickly, and ask them how fast they patched PHP2Shell.
- Keep PHP, your CMS, plugins and themes on supported versions.
- Keep tested backups, so a bad day is a restore rather than a rebuild.
- Read our ten-minute PHP2Shell safety check if you haven't already.
Her View
It is tempting to see AI as either a hero or a villain. This story shows something more ordinary: a powerful tool that magnifies whoever is holding it. The useful question for any business isn't "is AI dangerous?" but "are we organised enough to act within days, not months?"
 Also readClaude Can Now Remember You: Is This the Feature That Finally Makes It Feel Like a Real Assistant?→
His Insight
Security used to be partly protected by difficulty: bugs were hard to find, so many stayed buried. AI is removing that cushion. Over time, that should push the industry towards safer programming languages, faster update pipelines and better funding for the open-source projects everyone depends on. The transition, though, will be bumpy.
Related reading: PHP2Shell explained, can you trust an AI answer without checking sources? and website security basics.
Frequently asked questions
Did AI find PHP2Shell on its own?
No. Human researchers at Calif and Wiz used AI tools within their investigations and verified the results themselves. Calif also credited an independent researcher for the first discovery.
Will AI make hacking easier?
It can speed up parts of an attack, such as understanding a patch. That is why applying security updates quickly matters more now than before.
Can small businesses use AI for security?
Yes, carefully. AI tools can help review code and configurations, but findings should be checked by someone experienced before acting on them.
Is my website safer because of AI?
Only if the bugs AI helps find are actually patched on your server. Discovery helps nobody until the fix is installed.
Sources
H View stories follow our editorial policy. Spotted an error? Tell us and we will correct it.
Rate this article
One tap is enough. No comment needed.
Was this article helpful?
Your answer goes straight to our editors.
Comments0
No comments yet. Start the conversation.