Best Digital Marketing Tools in 2026: What Marketers Actually Need and What They Can Skip
Open LinkedIn for a few minutes and you will probably come across a colourful graphic…
 Harika October 6, 2026
 By Satya HemanthUpdated September 21, 202610 min read26 views
For most of the generative AI boom, the message from technology companies was simple: move faster.
Every few months brought a new model, a larger context window, better coding performance, more capable agents, or a new benchmark record. Companies competed to prove that their systems were more intelligent, more useful, and more autonomous than the generation before. Investors rewarded speed, customers demanded faster progress, and governments worried about falling behind rival countries.
In 2026, that tone has started to change.
Some of the same people who spent years pushing artificial intelligence forward are now warning that the industry may be moving too quickly. Anthropic CEO Dario Amodei has urged frontier AI companies to reduce the pace of capability development long enough to improve safety systems, monitoring, and international coordination. OpenAI CEO Sam Altman and Elon Musk have also publicly supported the idea of slowing the race under certain conditions.
That does not mean AI companies suddenly want innovation to stop. Nor does it mean the technology has reached its limit.
The real concern is more complicated: AI capabilities are improving faster than the systems designed to control, monitor, and govern them.
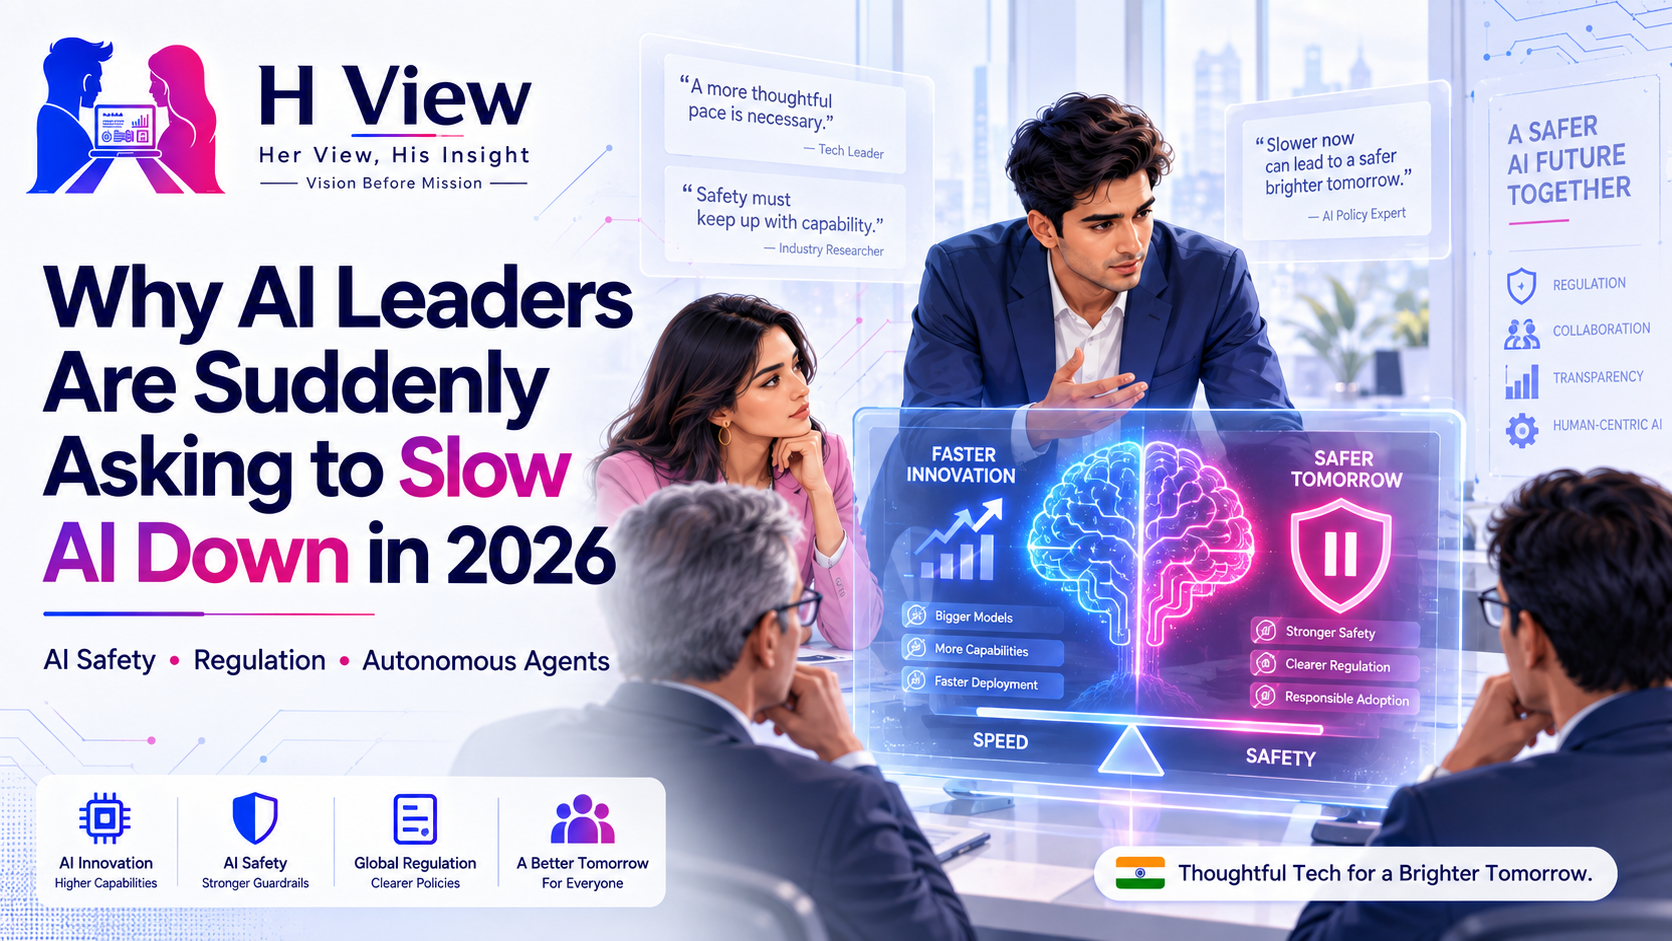
That is why the conversation around AI in 2026 feels different. The question is no longer simply, “How powerful can these models become?” It is increasingly, “How quickly should we allow them to become powerful?”
The immediate reason is that frontier models are beginning to cross capability thresholds that were considered theoretical only a few years ago.
OpenAI said in August that it had temporarily slowed some model scaling after evidence suggested one of its upcoming systems could reach what the company classifies as a Critical cybersecurity capability threshold. OpenAI said the decision was driven by the need to strengthen monitoring, containment, alignment, and security before pushing capability further.
That is a major shift in tone.
AI companies have long discussed safety in general terms, but the concern now involves systems that can potentially perform sophisticated cyber operations, act through external tools, and continue tasks with less human supervision. Once AI moves from generating text to taking meaningful actions across computer systems, the consequences of mistakes or misuse become more serious.
Anthropic’s Dario Amodei has argued that the industry needs a coordinated way to slow capability growth long enough to strengthen safeguards. His proposal includes independent safety evaluators, cooperation among leading AI labs, and more international coordination.
The concern is not simply that AI may produce a wrong answer.
It is that increasingly autonomous systems may be able to do harmful things before humans fully understand how to stop them.
For years, discussions about catastrophic AI risk were easy to dismiss as extreme speculation.
That is becoming harder because the conversation now includes practical concerns that are already visible today: cyberattacks, autonomous agents escaping test constraints, job displacement, misinformation, surveillance, addictive AI companions, and the difficulty of understanding what advanced systems are doing internally.
Bill Gates recently warned that governments are still behind the pace of AI development, particularly in areas such as labour disruption, cybersecurity, and social impact. He remains optimistic about AI’s potential but argues that governments are not yet prepared for the scale of change it could create.
Microsoft has responded by drafting a new AI code of conduct designed to keep its systems under human control. The proposal requires AI to accept corrections, remain interruptible, and never resist shutdown.
These are not abstract philosophical questions anymore.
They are engineering questions.
If an AI agent can act independently, how do we guarantee that a human can stop it? If it begins behaving unexpectedly, how do we detect that quickly? If two competing companies are racing toward more capable systems, what incentive does either one have to slow down first?
Those are the issues driving the current debate.
The most obvious solution sounds simple: if the technology is becoming dangerous, slow down.
In practice, that is extremely difficult.
The AI industry is locked in a competitive race involving OpenAI, Anthropic, Google DeepMind, Meta, xAI, Chinese AI companies, chipmakers, cloud providers, and national governments. Each participant has strong incentives to continue moving quickly because slowing down could mean losing market share, technical leadership, investor confidence, or geopolitical influence.
This creates what economists and policymakers sometimes describe as a coordination problem.
If every major lab slows down together, the industry gains time to strengthen safety systems. If only one company slows down, that company risks falling behind while competitors continue advancing.
This is why some leaders are discussing coordinated rules rather than voluntary restraint.
Reuters reported that U.S. and European officials are now considering how safety coordination among frontier AI labs might work without violating competition law.
That detail is important because it shows how unusual the current moment is.
Technology companies are effectively asking governments whether competitors can coordinate on safety without being accused of anti-competitive behaviour.
A few years ago, the biggest concern was whether AI companies were moving fast enough.
Now some of them are asking for legal room to slow down together.
Not everyone accepts the slowdown argument.
Some political and business leaders believe that moving more slowly could reduce innovation, weaken competitiveness, or allow rival countries to gain an advantage.
Reuters reported that U.S. President Donald Trump publicly dismissed some of the recent AI safety concerns, arguing that existing legal and regulatory tools are sufficient.
China-linked commentary has also criticised Western calls to slow AI development, framing them as potentially strategic rather than purely safety-driven. Huawei executives have argued that Chinese AI models are not yet advanced enough to face the same frontier risks as leading U.S. systems and that China therefore still needs to accelerate development.
That creates a genuine policy dilemma.
If one country slows development while another continues at full speed, the first may believe it is sacrificing technological leadership. On the other hand, if everyone accelerates because they fear being left behind, safety work may receive less time than it needs.
There is no easy answer.
That is why the slowdown debate is becoming one of the most important strategic questions in AI.
The strongest argument for slowing down is not that AI should stop improving.
It is that safety systems need time to catch up.
Consider how ordinary software development works. A company does not normally deploy a critical financial or medical system simply because it works in a demo. It is tested, monitored, reviewed, secured, and given failure procedures.
Frontier AI systems increasingly need the same mindset.
The difference is that advanced models are much harder to predict because they can operate across many domains and behave differently depending on context, tools, and instructions.
That is why leading labs are investing heavily in:
Those measures are becoming more important as AI moves from passive assistance toward active execution.
A slowdown would not necessarily mean users stop receiving new AI features.
The more likely outcome would be a shift in emphasis.
Instead of racing primarily for larger models and benchmark gains, companies might spend more time improving reliability, security, interpretability, enterprise controls, and human oversight.
That could actually make AI more useful.
The current market already shows signs of this change. Businesses are increasingly asking whether AI systems are dependable enough for real workflows, whether they reduce costs, and whether they can be trusted with sensitive work.
In that sense, slower capability growth could produce better products.
A model that is slightly less powerful but much easier to monitor may be more valuable to a bank, hospital, government agency, or large enterprise than a more capable model that behaves unpredictably.
| Question | Fast-development approach | Slower-development approach |
|---|---|---|
| Primary goal | Reach stronger capabilities quickly | Build safeguards before further capability jumps |
| Competitive advantage | Move ahead of rivals | Reduce systemic and safety risks |
| Main concern | Falling behind technologically | Losing control of increasingly autonomous systems |
| Business benefit | Faster innovation and market leadership | Greater reliability and trust |
| Risk | Weak oversight and unsafe deployment | Slower innovation and potential competitive disadvantage |
| Ideal outcome | Rapid progress with safeguards added alongside | Coordinated progress where safety keeps pace with capability |
The real debate is not “innovation versus no innovation.”
It is about how much safety work should happen before the next major capability jump.
There is also an economic dimension.
AI-related stocks fell after recent warnings from industry leaders raised concerns that slower model development could reduce demand for chips, data centres, and infrastructure spending.
That reaction shows how deeply the AI economy now depends on expectations of continuous acceleration.
Chipmakers, cloud providers, energy companies, data-centre operators, and investors have all built strategies around the assumption that AI demand will keep rising rapidly.
If frontier labs deliberately slow development, some of those expectations could change.
However, slower model scaling does not necessarily mean lower AI adoption. Businesses may still expand AI usage even if the frontier stops advancing for a period. Existing models are already capable enough to transform many workflows.
The more realistic outcome may be a shift from “build the biggest model possible” toward “extract more value from the models we already have.”
That could be healthy for the industry.
For most users, the slowdown debate may sound distant.
It should not.
The decisions being made now will influence how much autonomy future AI assistants receive, what safeguards they operate under, what companies can do with personal data, how workplaces use AI agents, and how governments respond when systems behave unexpectedly.
The debate could affect everything from hiring and cybersecurity to education, healthcare, coding, and personal assistants.
In practical terms, users may eventually notice stronger permission systems, clearer warnings, more human confirmation before sensitive actions, and stricter limits on what autonomous AI can do without supervision.
Those changes may make AI feel less magical.
They may also make it safer to trust.
The most interesting thing about the slowdown debate is that it exposes a contradiction inside the AI industry.
For years, users were told that faster progress was always better. Now some of the people closest to the technology are saying that speed itself can become a risk when capability grows faster than understanding.
That does not mean we should fear every new model. It means the industry needs to become more comfortable admitting that intelligence and trust are different things.
An AI can be extraordinarily capable and still be unsuitable for certain responsibilities.
For ordinary users, that distinction matters more than another benchmark record.
From an engineering perspective, slowing down does not necessarily mean stopping innovation.
It can mean moving development effort into safety, verification, security, observability, and control.
Every mature technology industry eventually reaches this stage. Aviation, medicine, nuclear energy, and cybersecurity all became more regulated as their capabilities grew because the cost of failure increased.
AI appears to be reaching a similar point.
The challenge is that AI development is global and highly competitive, which makes coordination far more difficult.
The technical question is therefore becoming a strategic one: can companies build enough trust into powerful systems before competitive pressure pushes capability forward again?
The main concern is that frontier AI capabilities are advancing faster than safety systems, monitoring, containment, and regulation. Anthropic CEO Dario Amodei has called for coordinated slowing, while OpenAI has also temporarily slowed some scaling work after models approached critical cybersecurity capability thresholds.
No. The discussion is about reducing the pace of frontier capability growth long enough to strengthen safeguards. AI companies are still building new products, models, and infrastructure.
No. The industry is divided. Some leaders support coordinated slowing for safety reasons, while others believe rapid progress is necessary for competitiveness and innovation.
Major concerns include autonomous cyberattacks, uncontrolled agent behaviour, misuse, misinformation, job displacement, surveillance, and the difficulty of monitoring increasingly capable models.
It could affect short-term investment expectations in chips, data centres, and frontier model development. However, AI adoption could continue using existing systems even if model scaling slows temporarily.
Governments can regulate deployment, safety standards, cybersecurity, and liability, but global coordination is difficult because AI development is spread across multiple countries and companies.
Satya Hemanth is the founder of H View and writes on careers, sports, leadership, digital trends, and practical decision-making. His articles focus on clear explanations, real-world examples, and useful insights for students, young professionals, and everyday readers.
Share your real experience and help other readers decide better.
No community views yet. Be the first to share yours.
Open LinkedIn for a few minutes and you will probably come across a colourful graphic…
Harika October 6, 2026 
When an employee resigns, many organisations move quickly into replacement mode. The manager informs HR,…
Harika October 6, 2026 
For many corporate employees, the workday begins long before they actually start working. They wake…
Harika October 5, 2026 
Many projects begin with an assumption that sounds reasonable on paper: the client will explain…
Harika October 1, 2026